FRP-SSH-Guard v0.0.7 is available
Slow-probe protection for forwarded ports, automatic administrator learning, and an activity log that explains why a source was banned.
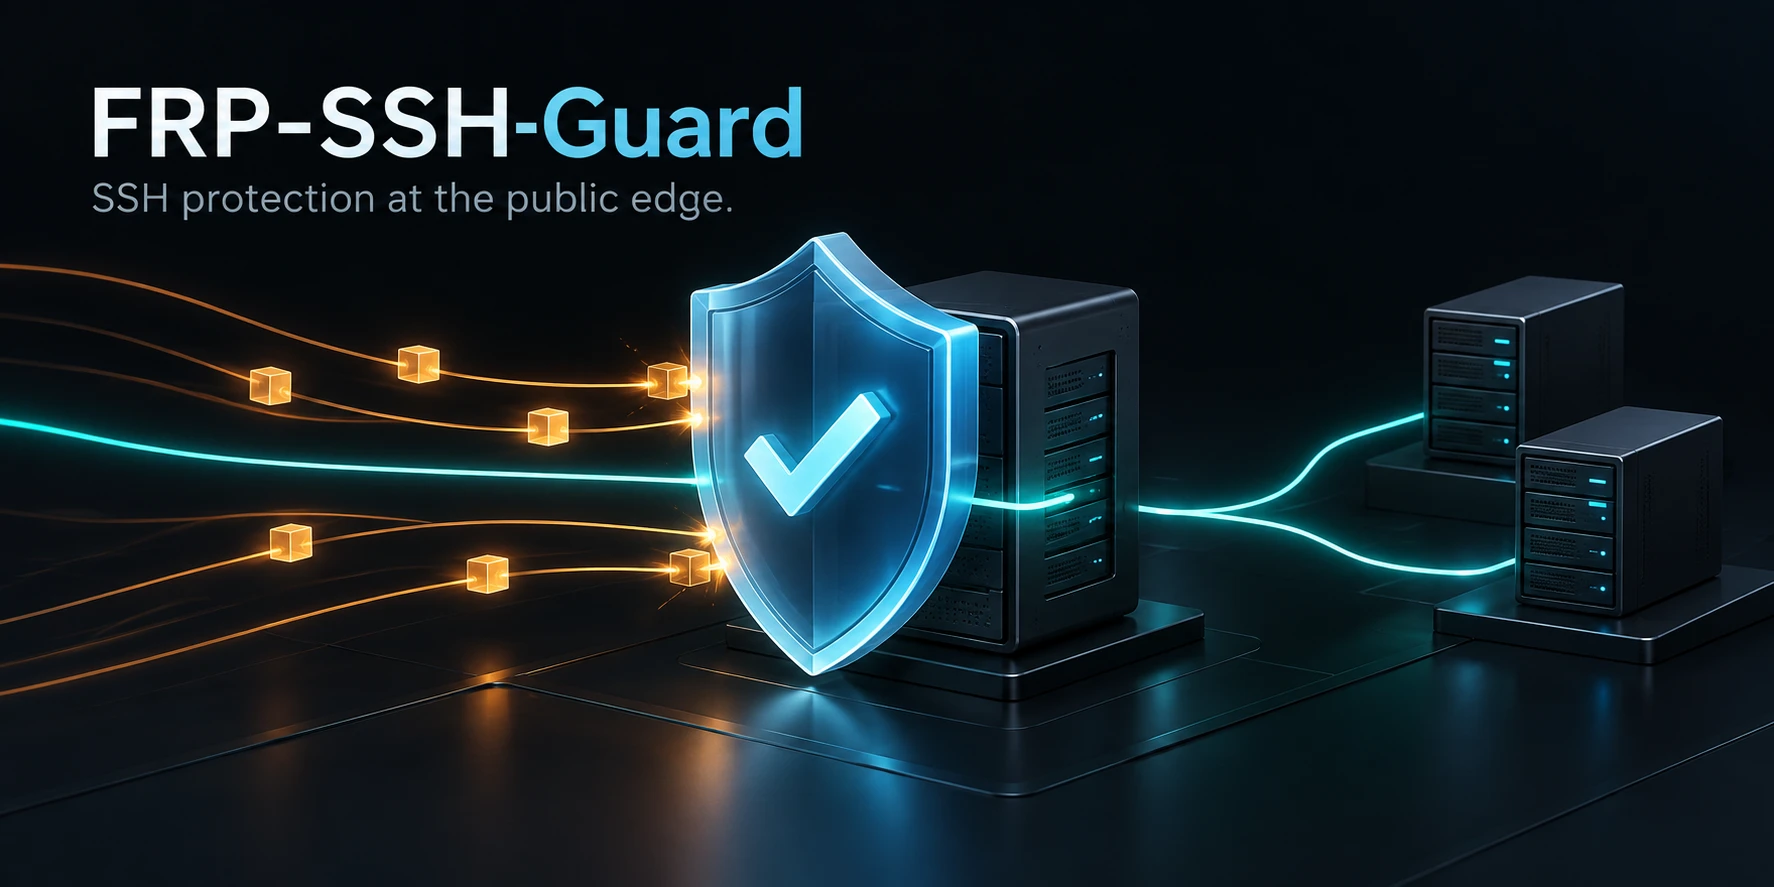
FRP-SSH-Guard v0.0.7 is now available. This update extends slow-probe protection to FRP-forwarded ports, simplifies its controls, and makes bans easier to understand. It also improves how the guard recognizes administrators and handles repeated offenses.
Download v0.0.7 · Explore the product
One switch for slow-probe protection
SSH_SLOW_PROTECTION=on/off replaces the old three-mode setting. When on, it detects, records, and bans; when off, slow detection is disabled. New installations default to on.
Forwarded ports now participate in this protection. With shared jails, the default threshold is more than 300 new connections from one source across forwarded ports over 24 hours. With separate jails, it is 100 on one port. Local port 22 retains its threshold of 20 failed logins over 24 hours when local SSH protection is enabled.
Forwarded authentication remains invisible to the guard: these are approximate, gradually refilling connection limits, and SYN retries count too. Sources whitelisted under any port are excluded from slow detection. Administrators who frequently connect to forwarded machines should be whitelisted before enabling it. See the deployment guide for configuration details.
Recognize administrators and explain bans
- Automatic administrator learning.
LEARN_ADMINS=on, enabled for new installs and upgrades, trusts the source IP after a successful login to the public server by root, the settings owner, or a member ofsudo,admin, orwheel. Further logins renew the default 90-day period. This learns a source address, not an identity inside an FRP tunnel. - Fewer false counts from key retries. Rejected attempts within a login that succeeds are excluded; rejected keys in a dropped connection count once per connection.
- A fuller activity log.
frp-ssh-guard.logreplacesalerts.log, with the reason, threshold, and end time for bans, plus manual actions, escalation, releases, and accepted settings.LOG_MAX_SIZEcontrols its size. - Clearer lists. Each port has one section, and redundant address/subnet entries no longer make nftables reject the entire rule set.
These changes are documented in the v0.0.7 changelog.
Upgrading from v0.0.6
Download frp-ssh-guard_0.0.7.deb and SHA256SUMS from the release page, then verify and install:
sha256sum --ignore-missing -c SHA256SUMS
sudo apt install ./frp-ssh-guard_0.0.7.deb
An active guard refreshes automatically. Fresh or disabled installations still need port configuration and activation. If you downloaded an earlier v0.0.7 package, download both files again.
The old enforce setting becomes on; observe, off, or a missing setting become off. There is no observation-only mode in v0.0.7. Existing configured ban durations remain, while fresh defaults are 12 hours, 3 days, 7 days, 30 days, and 90 days. Repeat-offender history is now measured from when a ban ends; rebuilding that history can lengthen existing repeat-offender bans at the next timer run.
Review the migration guide before adopting new settings, and apply configuration edits with check followed by reload. Platform coverage is recorded in the validation notes.
The v0.0.6 announcement remains available in the release history.