Introducing FRP-SSH-Guard
Our open-source SSH guard: why we built it, the first public release, and local SSH protection in v0.0.5.
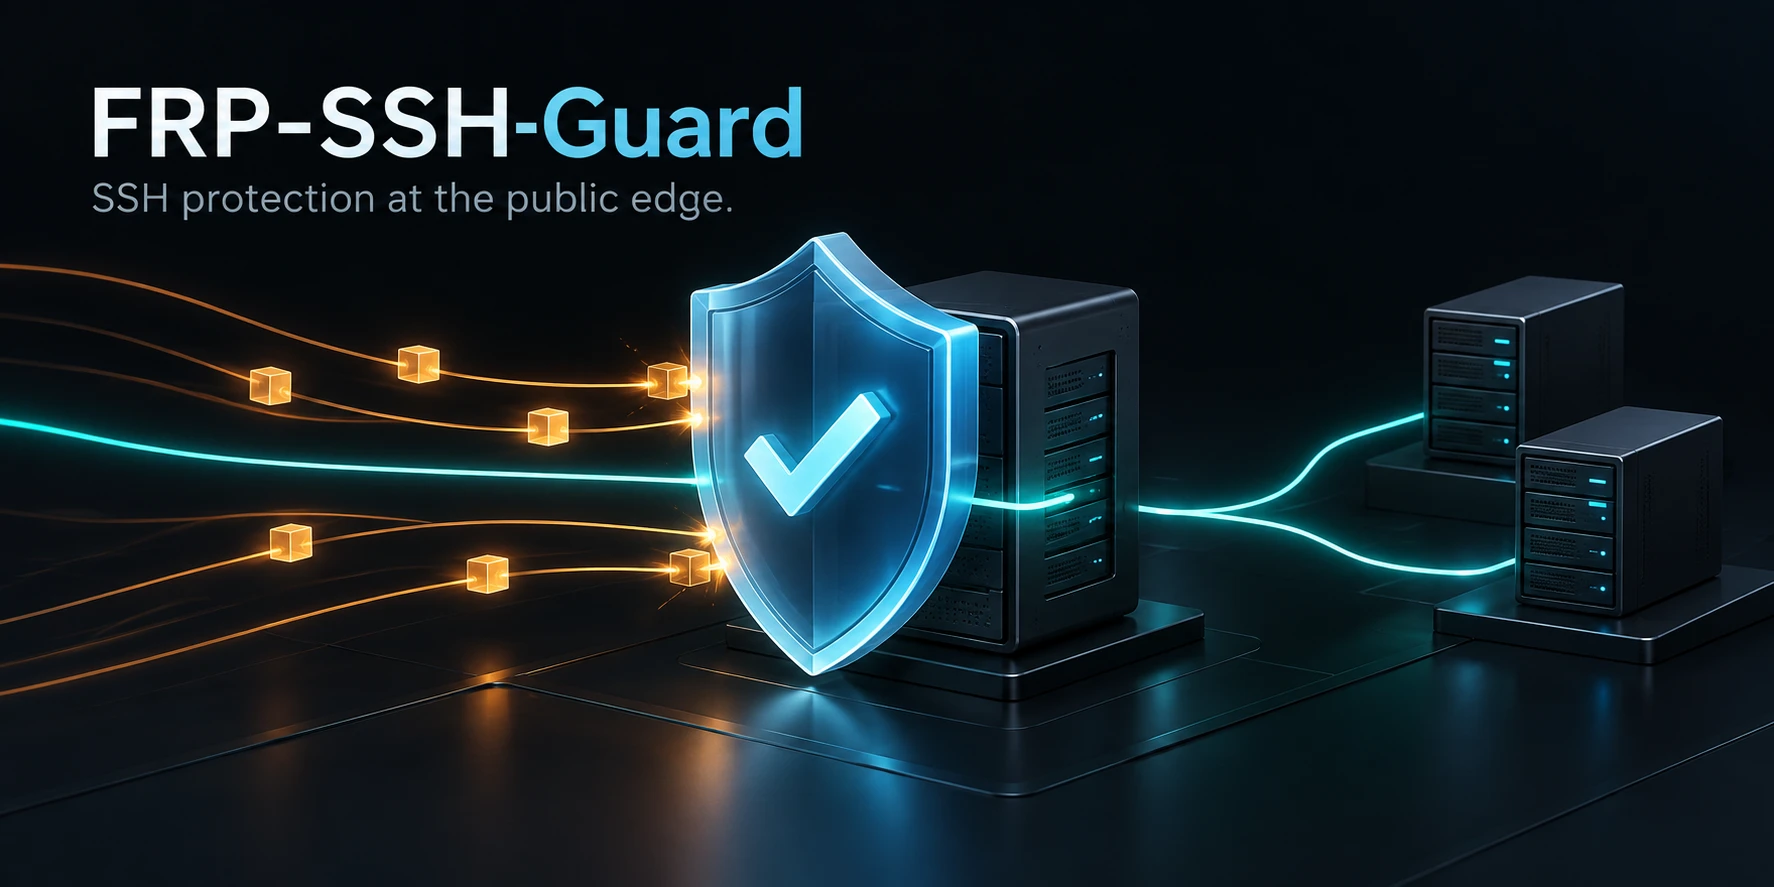
Running X-CAD behind FRP tunnels gave us a practical infrastructure problem: public SSH ports attract a steady stream of automated connection attempts. We built FRP-SSH-Guard to limit that traffic on the public server, before it reaches the private machines behind the tunnel.
The project is open source under the MIT license, with a Debian package, source code, and English and Chinese documentation. This post introduces the product and its first public releases. Explore the FRP-SSH-Guard product page.
What FRP-SSH-Guard does
Installed on the Linux host running frps, the guard uses nftables to limit new connections to the SSH ports you select. It combines per-source limits, a shared limit for each port, temporary bans, and longer bans for repeat offenders. IPv4 and IPv6 allow/block lists let administrators choose which sources to trust or restrict.
Forwarded SSH sessions stay encrypted: the guard cannot inspect their passwords or authentication results. Optional monitoring in v0.0.5 reads the public server’s own SSH logs, extending protection to its local port 22. The project README explains the deployment model and coverage.
v0.0.4 — the first public release
Released October 17, 2026 · Pre-release
Version 0.0.4 established the public package and an explicit configuration workflow. Administrators select protected ports in one commented settings file, validate the policy, and choose when to activate it.
- A Debian package and checksum, with complete source available from the release tag.
- Explicit enable, disable, and reload commands, plus an optional timed trial.
- Accepted settings retained for background tasks and reboot restoration; saving edits alone does not change active protection.
- Upgrade migration, configuration checks, and bilingual deployment guidance.
This version was published as a pre-release while full systemd and live FRP acceptance checks were still pending. Read the v0.0.4 release notes.
v0.0.5 — local SSH protection and easier administration
Released October 26, 2026
Version 0.0.5 expands protection and makes day-to-day management clearer:
- Optional protection for the server itself. Enable connection limits and detection of failed or invalid-user logins on local SSH port 22. This is off by default.
- Shared or separate bans. Keep a shared jail across protected ports, or isolate automatic bans and repeat-offender history by port.
- Settings and lists together. Editable configuration and combined manual/automatic allow/block lists live in
~/.frp-ssh-guard/, with scope, source labels, and expiry times. - More control over access. Manual blocks can be permanent or timed and apply to all protected ports or selected ports. Optional trusted-login learning supports password, public-key, and PAM authentication on the local server.
- Upgrades that retain configuration. Installation imports existing lists and bans and adds missing defaults without overwriting custom settings. The release notes explain migration details, including a timer caveat on the first upgrade from v0.0.4.
Installation does not activate new protection or apply pending settings automatically. Read the v0.0.5 release notes and download the package.
Latest release
v0.0.6 is now available. Its changes and upgrade instructions have their own release announcement.
For the current package, documentation, and project updates, visit the product page or follow FRP-SSH-Guard on GitHub.